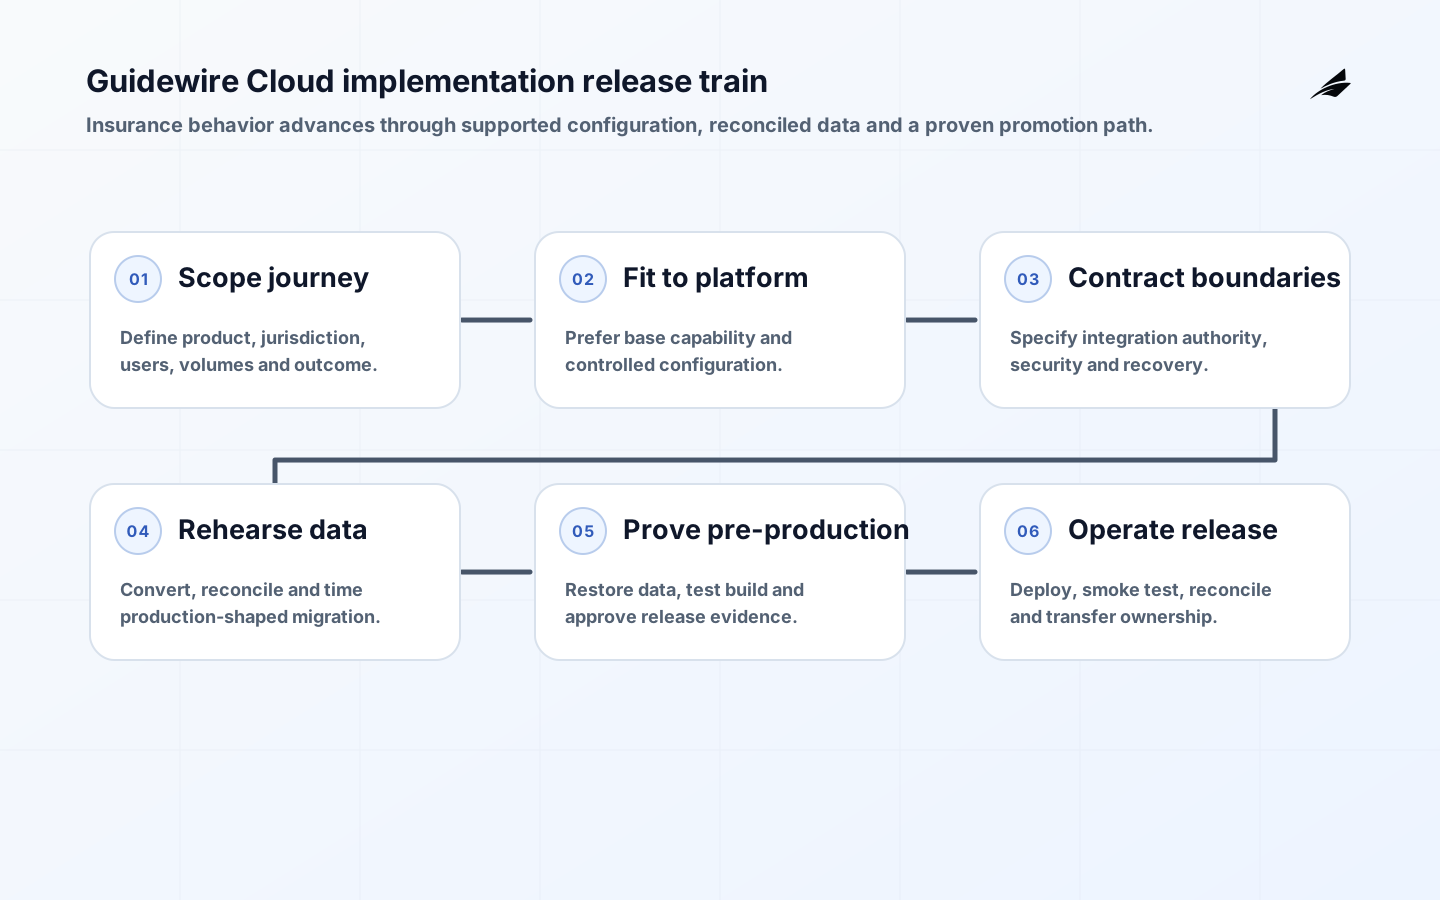
An insurance core system cloud migration is an operating-model change expressed through product configuration, integrations, data and releases. The migration must preserve policy, billing and claims outcomes while adopting the target platform's supported development and deployment path. Success is not simply moving applications to hosted infrastructure; it is reducing avoidable customization, proving business behavior and building an insurer team that can absorb continuing cloud releases.
This checklist should be tailored to the contracted products, cloud region, release and insurer obligations. Use it with the scope, cost and risk plan, the practical FAQ and the policy administration modernization checklist. Confirm current behavior in the supplier's official documentation and support channels before execution.
Define insurance outcomes and product scope
Select bounded journeys such as quote-to-bind, policy change, billing exception or first notice of loss through assignment. Define target products, jurisdictions, channels, users, volumes, service objectives and measurable outcomes. Inventory current rules, forms, integrations, reports, data, manual work and regulatory evidence. Separate capabilities required for day-one continuity from changes intended to improve the process.
Establish design authority across product, underwriting, claims, billing, architecture, data, security and operations. Decide how the program evaluates standard capability, configuration, extension, third-party solution and process change. Many suppliers publish development standards for their cloud products, describing principles and practices for quality, predictability and security; adopt the ones that apply. Record every departure with value, upgrade impact, owner and retirement trigger.
| Design choice | Preferred question | Evidence before approval |
|---|---|---|
| Use standard capability | Can the operating process adopt the supported behavior? | Fit demonstration and policy-owner acceptance |
| Configure | Is the variation supported without custom code? | Configuration design, tests and ownership |
| Extend | Does differentiated value justify lifecycle burden? | Architecture decision, assurance impact and upgrade test |
| Integrate | Which system owns the record and failure recovery? | Contract, security, idempotency and reconciliation |
| Migrate | Which history must be operationally active? | Retention, archive access and conversion rules |
| Retire legacy | What dependency or evidence remains? | Decommission checklist, archive proof and access removal |
Establish the cloud delivery model
A cloud platform typically provides development, build, deployment and observability capabilities, organized into accounts or subscriptions, environments, databases, authentication, build and promotion. Map the supplier's concepts to insurer environment policy, release authority and segregation of duties. Document which responsibilities belong to the cloud provider, the product supplier, the implementation partner and the insurer for code, configuration, identity, data and external services.
Provision access through individual identities and least privilege. Separate development work from promotion to pre-production and production. Inventory repositories, binary storage, CI/CD, certificates, secrets, variables and runtime properties. Define evidence retention for builds and deployments. Establish a current-release watch and a process for testing platform changes, deprecations and product updates against the insurer's configurations and integrations.
Control configuration and integration boundaries
Organize configuration around owned insurance capabilities and trace business rules to tests. Avoid copying legacy behavior without confirming current need. Keep rules, product model, forms and user experience coherent across policy, billing and claims. Review batch schedules and high-volume operations. Every custom component should have a named owner, supported interface, logging, performance expectation and upgrade compatibility strategy.
For integrations, specify direction, authoritative system, protocol, authentication, payload, privacy class, throughput, timeout, retry, idempotency, ordering and reconciliation. Connectivity options usually include public TLS endpoints and private connectivity between networks; confirm which the contract and region support. Test DNS, certificates, proxies, firewall paths, private endpoints and provider rate limits under production-shaped conditions.
| Integration class | Control focus | Failure exercise |
|---|---|---|
| Synchronous rating or identity | Latency, timeout, authentication and safe fallback | Dependency slow, unavailable or returns invalid schema |
| Asynchronous document or finance | Durability, ordering, duplicate handling and reconciliation | Consumer outage followed by controlled replay |
| Inbound API or portal | Authorization, tenant or account scope and abuse limits | Valid user attempts unauthorized object access |
| Outbound notification | Consent, template, provider response and idempotency | Provider timeout after accepting message |
| Data and analytics feed | Purpose, minimization, freshness and correction | Late or corrected source record |
| Batch or file exchange | Encryption, completeness, cutoff and quarantine | Partial, duplicate or malformed file |
Rehearse insurance data conversion and reconciliation
Classify policy, account, billing, claims, party, document, note, code and audit history by operational need, legal retention and archive access. Profile completeness, duplicates, invalid references, unsupported codes and date or currency semantics. Define transformation rules with business owners. Decide what migrates actively, what is summarized and what remains in a governed archive; preserve links users need to service customers and explain prior decisions.
Run repeatable conversion cycles with record counts, financial control totals, referential integrity, rejected-record queues and business sampling. Reconcile open policies, receivables, payments, reserves, recoveries and claim financials according to scope. Time extraction, load, validation and rollback. The final rehearsal should use production-shaped volume and the exact code and procedure intended for cutover. Retain signed discrepancy treatment and evidence.
Embed security, testing and deployment checks
Shared responsibility guidance from cloud and product suppliers usually states that the insurer is responsible for its own code and configurations even though the supplier manages the underlying platform. Threat-model custom code, integrations, document processing, administrative tools and secrets. Test role and object authorization, protect components and follow the supplier's policy on customer security testing.
Build a layered suite: rules and utilities, integration contracts, product-model and configuration tests, data-conversion tests, and end-to-end insurance journeys. Add accessibility, performance, batch, resilience and security evidence. Where the platform offers automated deployment checks, they can block promotion when required verification is not successful. Define insurer gates beyond platform checks, including business acceptance, reconciliation and support readiness.
Follow a rehearsed promotion and production release path
A typical production procedure describes preparation, dry run and production stages. Promote builds to pre-production, back up production, restore that data in pre-production, test, then promote the verified builds and run production smoke tests. Plan around maintenance windows and confirm current prerequisites with the supplier for the exact platform release.
- Freeze the release candidate and trace configuration, code, integration and migration versions.
- Promote to pre-production and restore an approved production backup under protected access.
- Run conversion, regression, performance, security, batch and end-to-end insurance tests.
- Review discrepancies, schema changes, deployment checks, settings, certificates and open risks.
- Approve business cutover, communication, support bridge, control totals and reversal criteria.
- Promote the verified build and deploy using the supported production procedure.
- Verify application and node status, execute business smoke tests and reconcile critical records.
- Stabilize under enhanced monitoring and close the release only after business acceptance.
Prepare insurer ownership and continuous cloud operation
Name owners for product configuration, integrations, data, security, release, incident response and the supplier relationship. Instrument critical insurance journeys and external dependencies, not just node health. Maintain runbooks for failed batch, interface backlog, document outage, identity failure and data correction. Review platform status, release notes, vulnerabilities, capacity, cloud usage and assurance findings on an agreed cadence.
Transfer knowledge through insurer participation in design, code review, release and incident exercises. Keep decisions and tests current, and maintain a backlog for reducing extensions that obstruct updates. Measure quote or claim outcomes, transaction correctness, release reliability, interface exceptions, support demand and update readiness. The migration should leave the insurer able to accept platform evolution without reopening the original transformation program.
Example: migrate open claims as a bounded wave
For a wave of open claims, define the scope first: lines of business, jurisdictions, claim statuses and age limits. Specify which claim facts, coverage snapshots, parties, reserves, payments, recoveries, notes and documents convert, and which stay in a governed archive with a link from the new claim record. Agree a freeze and cutoff rule for claims updated during conversion, and decide whether payments in flight complete in the old system or the new one. Make duplicate payment prevention, orphaned documents and unmatched parties explicit rather than leaving them for end-to-end testing.
Create conversion tests for each claim state, role tests for adjuster and supervisor access, and contract tests for payment and document integrations. In pre-production, run restored production-shaped data through the conversion, then reconcile reserve and payment totals by claim, line of business and period. Production smoke tests should verify a controlled claim path without exposing real customer information. After launch, measure payment delay, duplicate rate, reserve variance, reopened claims and support exceptions, and keep the old system read-only until reconciliation is signed off.
Key takeaways
- Frame the migration around bounded insurance journeys and measurable outcomes.
- Prefer supported standard capability and configuration; justify every extension by lifecycle value.
- Specify integration authority, failure behavior and reconciliation before development.
- Rehearse migration and the documented pre-production-to-production release path with real evidence.
- Build insurer ownership for continuing updates, operations and reduction of avoidable customization.
Frequently asked questions
When is a migration rehearsal good enough?
When it meets exit criteria agreed in advance: production-shaped volume, the exact cutover procedure and code, reconciled financial totals, timings that fit the window, and discrepancies either fixed or signed off by their owners. A rehearsal that only proves the load completes is not enough.
How do we know the legacy system can be switched off?
When usage, interfaces, reports, retention duties and audit evidence have been confirmed against a decommission checklist, archived records can answer real historical questions, and access has been removed. Fund the switch-off as a release outcome with an owner and a date.
What should an implementation partner hand over?
At minimum: source and history, configuration, integration contracts, conversion rules, tests, build and promotion knowledge, architecture decisions, security evidence, runbooks, licenses, known risks and training. Verify by having the insurer team deploy, diagnose and change a representative capability using its own access.
Conclusion
After each cloud update, record compatibility findings for configurations and integrations, remediation effort and escaped issues. Trend that evidence to identify extensions that deserve redesign or retirement.
A cloud migration of core insurance systems is dependable when insurance outcomes, supported platform practices and insurer ownership reinforce each other. Keep configuration close to the product, make integrations and migration reconcilable, follow the supplier's current promotion procedure and test operational recovery. That foundation turns cloud delivery into a sustainable release train rather than a one-time migration event.