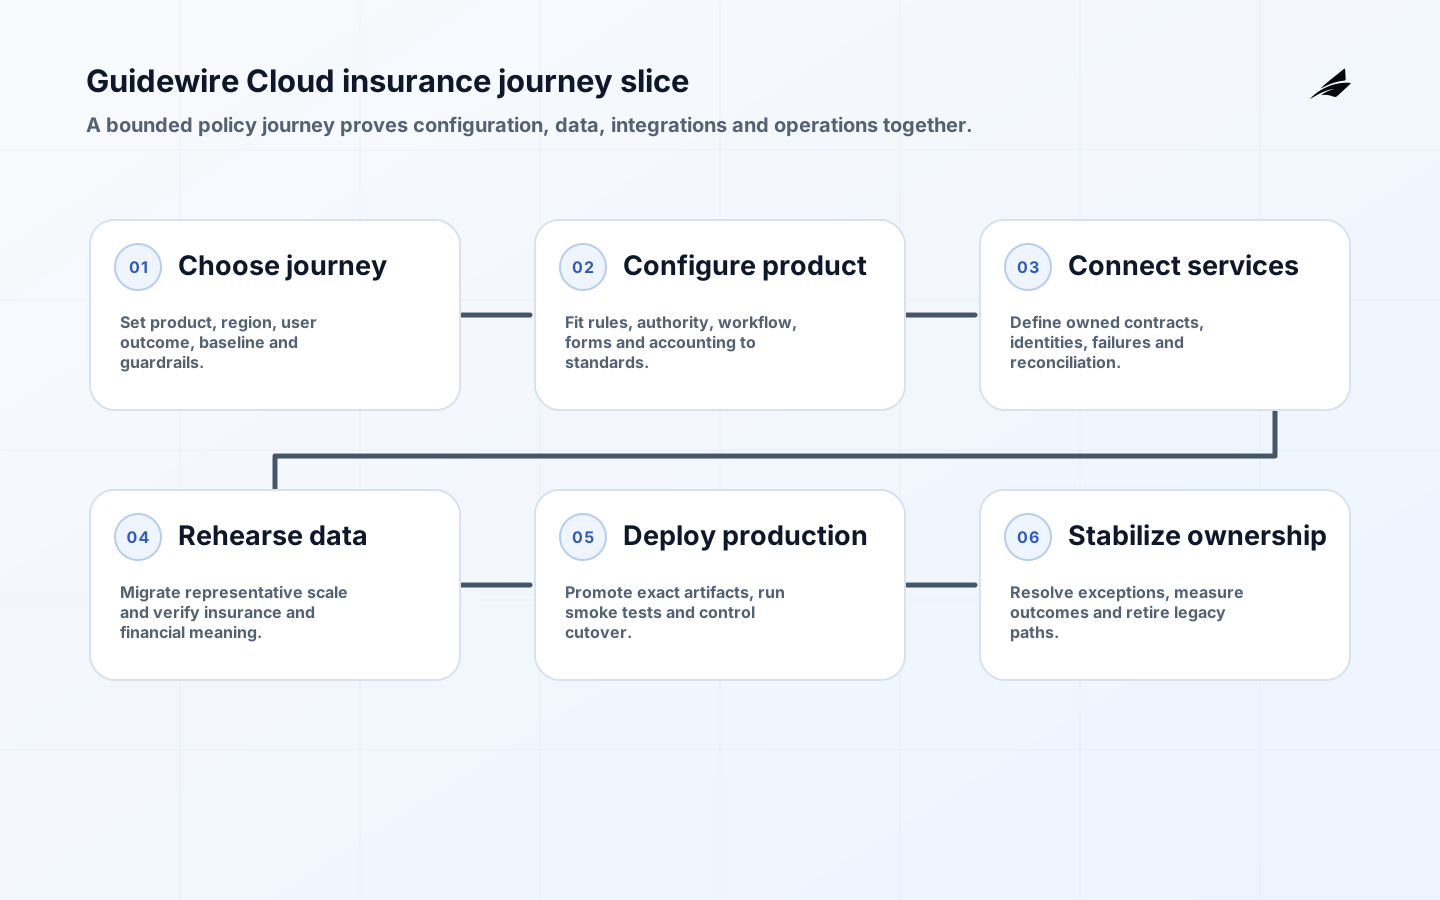
Moving an insurer's core systems to the cloud is a core insurance change program, not an infrastructure move. Policy, billing and claims behavior must be redesigned or confirmed; products and authority need configuration; data must reconcile; integrations must survive change; and operations must adopt a new release, access and support model. The program succeeds when a bounded insurance journey works in production with traceable financial and customer outcomes, not when a new environment is provisioned.
This plan is for insurers moving policy, billing and claims platforms to the cloud, whether the target is infrastructure the insurer runs, a vendor-hosted product or a software-as-a-service core. Use the implementation checklist for execution and the practical FAQ for stakeholder decisions. Teams comparing operating models can also review the guide to managed cloud services for insurance core platforms. Product capabilities and contract terms differ by supplier and change over time, so confirm current supplier documentation and the insurer's agreement at each architecture and release decision.
Frame the insurance business case
Define the line of business, jurisdictions, distribution channels and operational outcome. Useful goals include shortening product change lead time, improving straight-through processing, giving adjusters a coherent claim workspace, reducing billing exceptions or retiring unsupported core infrastructure. Establish current cycle time, leakage, manual touches, defect, outage, operating cost and customer measures. Separate benefits created by the move to the cloud from benefits that depend on process, data or organization change.
| Business decision | Evidence needed | Named owner |
|---|---|---|
| Initial product and region | Volume, complexity, learning value and dependency map | Business sponsor |
| Target operating process | Current exceptions and approved future workflow | Operations lead |
| Treatment policy | Migration principles and exception authority | Product owner |
| Conversion and transition approach | Book characteristics, data quality and transition risk | Data owner |
| Success measures | Baseline, target, guardrails and measurement source | Benefits owner |
Build the roadmap around complete insurance journeys, such as quote-bind-issue, endorsement, renewal, invoice-payment or first-notice-to-claim-payment. A journey exposes product, workflow, documents, permissions, accounting, data and integrations together. Module-by-module plans can report progress while postponing the cross-system risks until late integration.
Set scope and migration treatment rules
Inventory products, forms, rules, roles, authority, reports, interfaces, batch work, data and regulatory variation. Classify each item as rehost, replatform, replace, integrate or retire. Require a business rationale and a lifecycle owner for every exception to the standard treatment. Recreating a legacy screen or workaround preserves cost and complicates future change. Equally, forcing a standard flow that breaks a necessary underwriting or claims control creates operational risk.
| Treatment | Choose when | Approval evidence |
|---|---|---|
| Rehost | The application is stable and supported but needs a new home first | Dependency map, licensing check and recovery design |
| Replatform | Managed cloud services can replace hosting, database or batch components without changing business behavior | Regression results, performance baseline and support model |
| Replace | A supported product or service provides the capability and the process can adopt it | Demonstrated scenarios and operations acceptance |
| Integrate | Another system remains authoritative or provides a service | Contract, ownership, failure and reconciliation design |
| Retire | Report, interface or workaround is no longer needed | Usage, retention and dependency confirmation |
Create an exception budget and review it by journey. Complexity accumulates through small decisions in rules, plugins, integrations and data model changes. Record the supported mechanism, owner, tests and removal trigger. Review the target platform's current standards and implementation guidance; do not rely on patterns carried forward from an older self-managed environment without validation.
Define the target cloud delivery model
Whatever the hosting model, the program needs a written description of how the target environment is built, deployed, accessed and observed. Initial provisioning usually covers a landing zone, network connectivity, identity federation, a CI/CD path and database services, while the insurer applies its own configuration and integrations. Define development, test, pre-production and production environments with controlled build promotion, then translate that model into the insurer's branch, release, access, evidence and support procedures.
- Confirm contracted services, environments, regions, limits and responsibilities.
- Federate workforce identity and automate lifecycle where supported; avoid shared engineering accounts.
- Define repository, branching, review, build promotion and artifact ownership.
- Separate environment configuration, certificates, secrets and runtime properties from source.
- Map cloud provider, product supplier, implementation partner and insurer support boundaries for every operational component.
- Make review of current supplier documentation and release notes part of architecture governance.
Keep an insurer-owned architecture map for core applications, integration services, digital experiences, data services and external platforms. Supplier diagrams explain the platform, not the insurer's complete service. Add payment, document, identity, rating, fraud, repair, banking, regulatory and analytics dependencies with their owners and recovery behavior.
Design data conversion and integrations together
Profile policy, account, billing, claim, contact, document, producer and reference data early. Decide which history must be operationally available, which can be archived with usable access, and which should not be moved. Define source-to-target keys, transformations, defaults, code mappings, financial reconciliation and exception ownership. Row counts are insufficient: premiums, receivables, payments, reserves and claim transactions need business totals and sample traceability.
| Integration pattern | Use | Control |
|---|---|---|
| Synchronous API | Immediate lookup or validated command | Timeout, authentication, idempotency and error contract |
| Asynchronous event | Durable state change and decoupled consumers | Schema version, duplicate handling and replay |
| Batch exchange | High-volume or scheduled partner flow | Manifest, completeness, cutoff and reconciliation |
| User link or embedded flow | Specialist experience outside core | Identity propagation, context and session failure |
| Analytical export | Reporting, actuarial or data science | Lineage, privacy, latency and semantic ownership |
Assign one system of record for each state transition. Avoid uncontrolled dual writes between old and new cores during coexistence. If a temporary bridge is required, use durable identifiers and reconciliation, and date its retirement. Test the network paths between the cloud and systems that stay on premises, including latency, bulk-load bandwidth and private connectivity, along with partner limits, delayed responses, duplicate messages and outage recovery. An integration is complete only when support can diagnose it and business owners can reconcile its effects.
Implement shared security responsibilities
Cloud providers and product suppliers typically publish a shared responsibility model: the provider secures the underlying cloud foundation while the customer retains application-level responsibilities. Confirm the current contractual model rather than inferring it. The insurer should own role design, least privilege, joiner-mover-leaver processes, secrets and certificates under its control, integration identities, data classification, application configuration, security monitoring and incident coordination.
| Control area | Implementation question | Evidence |
|---|---|---|
| Business authority | Can users approve only the right product, amount and jurisdiction? | Role matrix and negative tests |
| Privileged access | Is elevation individual, time-bound and auditable? | Access review and session record |
| Integration identity | Does each service have narrow independent permissions? | Credential inventory and rotation test |
| Sensitive data | Are access, masking, export and retention purpose-bound? | Data-flow and lifecycle verification |
| Incident response | Can the insurer and its suppliers coordinate quickly? | Joint scenario and contact validation |
Threat-model customer portals, producer access, service accounts, document and payment paths, and custom extensions. Test authorization at service boundaries, not only through screens. Preserve logs needed for fraud, security and audit while applying privacy and retention rules. Track security exceptions to an owner and expiry, especially when migration deadlines create pressure for broad temporary access.
Build production-quality release evidence
Create layered tests for product rules, rating, underwriting authority, billing, claim financials, documents, integrations, migration, performance, security and critical journeys. Build reusable product examples with expected premiums, forms, transactions and accounting. Automate deterministic regression, then use skilled exploratory testing for complex adjuster, underwriter and billing scenarios. Include accessibility and operational usability in customer and staff experiences.
A sound production deployment procedure covers preparation, pre-production dry runs using a restored copy of production data, build promotion, smoke tests and deployment verification, with rollback behavior that depends on the type of change. Build the program runbook from the target platform's current release procedure and the contract. Rehearse with production-scale data, exact artifacts, certificates and integrations; measure each step and define the point of no return.
- Promote the exact reviewed build and configuration through controlled environments.
- Restore and protect production-derived data according to insurer policy.
- Run migration, batch, integration and high-value journey reconciliation in the rehearsal.
- Verify application status, nodes, smoke tests and business transaction totals after deployment.
- Prepare rollback, forward-fix and communication paths for each failure class.
- Require business, technology, security and operations owners to accept evidence before cutover.
Cut over by controlled business wave
Choose transition by product, state, cohort or renewal where the insurance book permits. A big-bang conversion may simplify coexistence but concentrates data, integration and operational risk. Phased migration reduces concentration while requiring routing and cross-system service. Decide how call-center staff, producers, adjusters, finance and reporting locate the authoritative record during the transition.
Create a command center with one incident taxonomy and decision authority. Monitor quote, bind, issue, payment, document, claim and financial flows, not merely application health. Route data and integration exceptions to teams that can correct and reconcile them. Define stabilization exit using error rate, backlog, manual work, user proficiency, customer impact and close-cycle evidence. Transfer the remaining work into durable product and platform teams rather than dissolving knowledge at go-live.
Estimate cost and manage the largest risks
Total cost includes subscription, usage and cloud consumption terms, implementation partner, insurer product experts, data remediation, integrations, environments, testing, security, training, change, cutover, dual running and post-launch product ownership. Model volume, growth and optional services under the current contract, and give cloud consumption an owner from the first environment, since idle test environments and oversized data stores add cost quietly. Compare against avoided legacy infrastructure, upgrade, license and operational cost, but do not count savings until the old systems, interfaces and contracts are actually retired.
| Risk | Early indicator | Response |
|---|---|---|
| Legacy replication | Rising exception count and unchanged process | Treatment review with business authority |
| Data surprise | Unowned mappings and growing exceptions | Profile earlier and rehearse reconciliation |
| Integration fragility | Late contracts and manual recovery | Build journey slices and failure tests |
| Release bottleneck | Large branches and unstable regression | Smaller changes, automation and current platform guidance |
| Operational rejection | Training without role practice and duplicate work | Involve users, simplify workflow and support waves |
| Perpetual coexistence | No retirement owner or date | Fund decommissioning as a release outcome |
Key takeaways
- Treat the migration as an insurance operating-model and core-system change, not a hosting move.
- Scope complete insurance journeys and govern every rehost, replatform, replace, integrate or retire decision.
- Reconcile financial and operational meaning, not only migrated record counts.
- Adopt the target platform's promotion and security model while owning insurer-specific controls.
- Rehearse production, support transition waves and fund legacy retirement explicitly.
Frequently asked questions
How much customization should the cloud target allow?
Cloud platforms generally support configuration, integrations and supported extension mechanisms, subject to the supplier's standards and the contract. Use the least complex supported mechanism and justify extensions through business value, security, testing and future-change cost.
Should all historical policy and claim data migrate?
Not automatically. Decide from operational need, customer service, regulation, litigation, analytics and archive usability. Prove that retained history remains accessible and linked without loading low-value complexity into the new core.
How long does an insurance core cloud migration take?
Duration depends on products, regions, data quality, integrations, exceptions, testing and transition strategy. Estimate by journey and evidence gate. A narrow product wave can deliver learning earlier than a portfolio-wide cutover.
What should an implementation partner own?
The partner can lead configuration, engineering, migration and integration delivery, but insurer owners must retain product, risk, data, architecture and release decisions. Require transparent artifacts, skills that match the target platform and continuous knowledge transfer.
Conclusion
Moving core insurance systems to the cloud can provide a modern delivery and operating foundation for policy, billing and claims workflows, but value comes from disciplined insurance design and transition. Bounded journeys, treatment governance, reconciled data, resilient integrations, shared security and rehearsed production evidence give the program a credible route from a provisioned environment to dependable insurance operation.